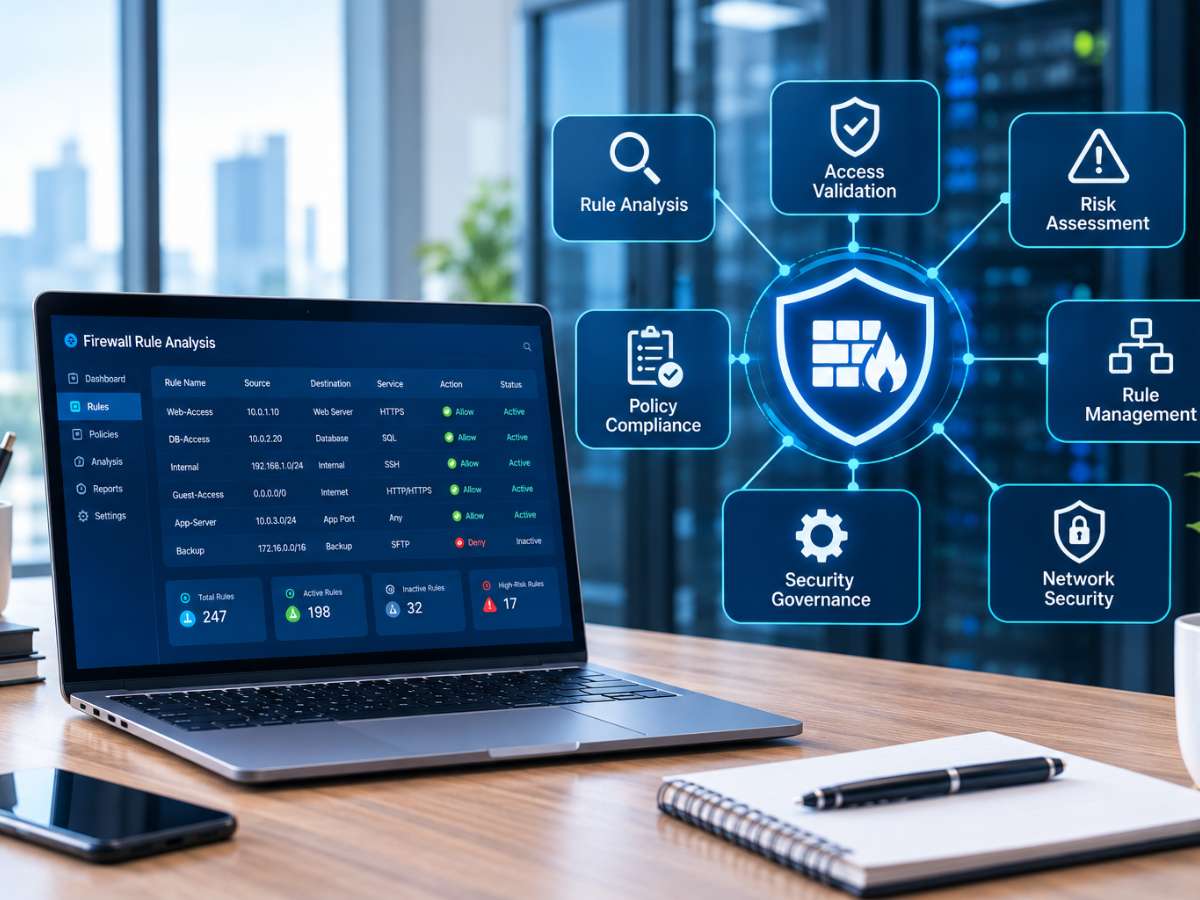
Firewall rules help organizations control network traffic, protect sensitive information, and limit access to critical systems. However, even a well configured firewall can leave security gaps when access permissions are not regularly reviewed, rule changes are poorly documented, or outdated policies remain active. Effective firewall access validation helps security teams confirm that each rule serves a legitimate business purpose and follows the organization’s security requirements.
In this blog, you will discover the most common firewall access validation gaps, why they matter, and how security teams can identify and address them. You will also learn how firewall change management automation, policy analysis, and compliance focused workflows can improve visibility and reduce unnecessary risk.
Understanding Firewall Access Validation
A firewall acts as a security checkpoint between networks, systems, applications, and external connections. Its rules determine which traffic can enter, leave, or move between different parts of an organization’s IT environment.
Firewall access validation is the process of checking whether those rules are necessary, correctly configured, appropriately authorized, and aligned with business and security requirements.
For example, a retailer might allow its payment application to communicate with an approved payment processor while blocking unnecessary access to internal systems. If a firewall rule grants broader access than the application requires, the business could expose sensitive systems to avoidable threats.
Validation involves more than checking whether a firewall is operational. Security teams must understand why each rule exists, which systems it affects, who approved it, and whether it still supports a legitimate business requirement.
This becomes particularly important in organizations managing multiple firewalls, cloud environments, remote locations, and frequent configuration changes. As environments grow, manually reviewing every rule becomes more difficult and time consuming.
Why Firewall Validation Gaps Create Security Risks
Firewall policies rarely remain unchanged forever. Applications are updated, employees change roles, business units adopt new services, and infrastructure moves between environments. Each change can introduce new access requirements.
Problems emerge when firewall rules are added without adequate review or when existing permissions are never reassessed.
An outdated rule might allow traffic from an unnecessarily broad network range. Another rule could permit access to a service that no longer exists. In other cases, conflicting rules may make it difficult for security teams to understand which policy actually governs a connection.
These weaknesses can increase the risk of unauthorized access, lateral movement, configuration errors, and compliance failures.
A structured network security risk assessment can help organizations identify which weaknesses deserve immediate attention. Rather than treating every firewall rule equally, teams can prioritize excessive permissions, access to sensitive assets, unexplained exceptions, and rules that conflict with internal security policies.
The objective is not to block all traffic. It is to ensure that every permitted connection has a clear purpose, an appropriate scope, and a defensible business justification.
Seven Common Firewall Access Validation Gaps
1. Overly Permissive Firewall Rules
One of the most common weaknesses is allowing more traffic than a business actually needs. Rules that permit access from an entire network instead of specific trusted systems can create unnecessary exposure.
For example, a retail business may need its inventory application to communicate with a database server. If the firewall allows every device on the office network to reach that database, a compromised workstation could gain an additional route to sensitive information.
Security teams should review source addresses, destination addresses, permitted services, ports, and connection directions. The principle of least privilege should guide each decision, allowing only the access required for a legitimate task.
A firewall analyzer can help identify overly permissive rules and highlight configurations that deserve closer investigation. However, a finding should always be checked against application requirements before a rule is changed.
2. Unused, Expired, and Forgotten Rules
Temporary firewall permissions have a habit of becoming permanent. A development team may request access for testing, an external consultant may need a short term connection, or a vendor may require access during installation. Once the work is finished, nobody may remember to remove the associated rule.
Unused rules increase complexity and make it harder to understand the actual security policy. Expired permissions can also remain active when there is no clear ownership or scheduled review process.
Security teams should identify rules that have not been used, check their original purpose, and verify whether the associated application or service still exists. It is important to distinguish genuinely unnecessary rules from legitimate rules that are used infrequently, such as disaster recovery connections.
3. Missing Business Justification and Ownership
A firewall rule should have a clear reason for existing. Unfortunately, some rules contain little more than a technical description, with no record of the business owner, requesting team, approval, or intended duration.
Imagine a shop owner who hires a third party to upgrade a point of sale system. The IT team opens a connection to support the installation, but the rule description simply says “vendor access.” Six months later, another administrator sees the rule and cannot determine whether it is still necessary.
Without ownership information, teams may hesitate to remove a risky rule because they fear disrupting an important service. They may also struggle to establish accountability during an investigation or audit.
A stronger validation process records the business purpose, requesting team, technical owner, approver, scope, and review date. Where appropriate, rules should have expiry dates and a named person responsible for confirming that access remains necessary.
This information turns firewall access validation from a purely technical exercise into a repeatable governance process.
4. Shadowed, Duplicate, and Conflicting Rules
Firewall rule order can affect how traffic is evaluated. A broad rule placed before a more specific rule may prevent the specific rule from being reached. This is commonly described as rule shadowing.
Duplicate rules can also accumulate when different administrators make similar changes without reviewing existing policies. Conflicting entries may leave teams uncertain about the intended configuration or make future maintenance unnecessarily difficult.
Consider a business that introduces a restrictive rule for a payment server but already has a broader permission covering the same destination. If the broader rule takes precedence, the intended restriction might not deliver the expected result.
Security teams should inspect rule order, overlapping address ranges, service definitions, and policy evaluation behavior. They should also verify the effect of any proposed change before implementing it.
An effective firewall rule compliance tool should help surface these issues and make the findings understandable enough for administrators to investigate and resolve safely.
5. Inadequate Validation of Firewall Changes
A firewall rule can be appropriate when requested but unsafe when implemented incorrectly. An incorrect IP address, an overly broad port range, or an unintended destination can turn an ordinary change into a security weakness.
Manual processes make this more likely, particularly when requests arrive through email or chat and administrators must translate them into technical configurations.
Firewall change automation can introduce consistent checks before a change reaches production. Depending on the workflow, these checks can include approval requirements, policy conflict detection, rule analysis, and verification of the requested scope.
Automation should not remove human judgment from high risk decisions. Instead, it should help security teams apply the same standards consistently and record who approved each action.
Opinnate explains its approach to automating firewall policy changes safely, including controlled workflows, validation, and change traceability.
6. Insufficient Logging and Monitoring
A firewall rule may appear reasonable on paper, but security teams also need sufficient visibility into how it is used. If logging is disabled where it is required, administrators may struggle to investigate unexpected connections or establish whether a permission is still needed.
For example, an organization may allow access to an internal server from a remote office. If suspicious traffic begins using that route, missing logs can make it harder to reconstruct what happened and determine the scope of the incident.
Teams should review logging settings, log collection, retention, alerting, and access to relevant records. Logging must be configured in line with security requirements, operational needs, and applicable privacy obligations.
Where usage data is available, it can also help teams identify unusual access patterns and investigate rules that appear unnecessary. However, a lack of recent traffic does not automatically prove that a rule is safe to remove.
7. Inconsistent Compliance and Risk Reviews
Firewall rules may need to satisfy internal security policies, contractual commitments, and regulatory requirements. When reviews are conducted inconsistently, a rule that violates an internal standard may remain active simply because nobody has assessed it recently.
A rule permitting an unapproved service, for instance, could conflict with an organization’s security policy even if the connection appears to work correctly.
Security teams should define review criteria, assign responsibility, document exceptions, and retain evidence of the checks performed. Relevant requirements will depend on the organization, its industry, the systems involved, and the applicable regulations.
A firewall rule compliance tool can help standardize reviews and generate reports that support internal governance and audit preparation. The team should still verify the scope and accuracy of those reports before treating them as evidence of compliance.
A structured network security risk assessment can further help prioritize issues based on factors such as rule permissiveness, logging, risky services, and conflicts with corporate policy.
Choosing the Right Firewall Management Approach
Not every organization needs the same level of automation. The right approach depends on the size of the environment, the frequency of firewall changes, the complexity of security policies, and the team’s available resources.
A small organization with a limited number of firewalls may begin with a documented review process and scheduled policy analysis. A larger organization managing multiple locations, firewall vendors, and sensitive workloads may benefit from centralized visibility, automated reporting, and controlled change workflows.
When evaluating firewall management solutions, consider the following factors.
- Policy visibility: Can administrators review rules across the relevant firewalls from a central location?
- Analysis capabilities: Can the platform identify unused, expired, shadowed, permissive, and conflicting rules?
- Compliance reporting: Can teams produce useful reports that support internal policies and applicable standards?
- Change governance: Does the solution support appropriate approvals, change tracking, and accountability?
- Operational fit: Can the solution work with existing processes and supported firewall environments without creating unnecessary complexity?
- Automation controls: Can routine actions be automated while keeping appropriate safeguards around sensitive changes?
An effective firewall analyzer should provide actionable findings rather than simply generating a long list of technical alerts. Teams need enough context to understand why a rule deserves attention and how to investigate it.
The goal is not to automate every decision. It is to make reviews more consistent, reduce repetitive work, and help security professionals focus their attention where it matters most.
When Your Security Team Needs a Closer Review
Certain operational changes should prompt security teams to reassess their firewall policies rather than waiting for the next scheduled audit. These situations include:
- After an application migration: New infrastructure may change IP addresses, communication paths, or access requirements, leaving old rules behind.
- Following a merger or acquisition: Different environments and policy standards can introduce duplicate permissions, conflicting rules, and inconsistent ownership.
- When onboarding a new service provider: External access should have a documented purpose, appropriate restrictions, and a clear review date.
- After a security incident: Teams should investigate whether existing permissions contributed to the incident and whether similar exposure exists elsewhere.
- Before an important audit: Reviewing rules and collecting evidence early can help identify missing documentation and unresolved policy exceptions.
- When change requests become difficult to manage: Frequent manual errors, delayed approvals, and limited visibility may indicate that existing processes need improvement.
These triggers provide practical opportunities to strengthen firewall governance. They also help teams connect access reviews with actual business changes instead of treating validation as an isolated administrative task.
Turn Firewall Visibility Into Stronger Security
Firewall security depends on more than creating rules and confirming that systems can communicate. Permissions must remain appropriate as applications, infrastructure, and business requirements change.
Regular firewall access validation helps teams identify excessive permissions, remove unnecessary rules, investigate policy conflicts, and maintain reliable evidence of important decisions. Combining structured reviews with risk based prioritization and appropriate automation can also reduce administrative effort without sacrificing oversight.
For organizations managing complex firewall environments, Opinnate offers capabilities designed to support policy analysis, compliance reporting, optimization, and controlled changes.
Ready to improve your firewall policy management process? Explore Opinnate’s firewall management capabilities or request a demo to see how policy visibility and workflow automation could support your security team’s requirements.
Frequently Asked Questions
1. What is firewall access validation?
Firewall access validation is the process of checking whether firewall rules are necessary, correctly configured, properly authorized, and aligned with security policies. It helps organizations identify excessive permissions and outdated access.
2. How often should firewall rules be reviewed?
Review frequency depends on business risk, regulatory requirements, and the rate of change in the environment. High risk rules should receive closer attention, while scheduled reviews and event driven checks help maintain ongoing oversight.
3. What are the most common firewall validation gaps?
Common gaps include overly permissive rules, expired permissions, missing ownership information, shadowed or duplicate rules, inadequate logging, and changes implemented without sufficient validation or approval.
4. How does firewall change management automation help?
It can standardize approval workflows, support pre deployment checks, track changes, and maintain audit records. Automation improves consistency, but sensitive decisions still require appropriate human oversight.
5. Can a firewall analyzer help with compliance?
Yes. A firewall analyzer can identify potentially non compliant rules, highlight policy conflicts, and support reporting. Organizations must still validate findings against applicable requirements and retain appropriate evidence of their review.